
How reusable, issuer-backed proofs can reduce repeated document collection while keeping platform decisions scoped and accountable.
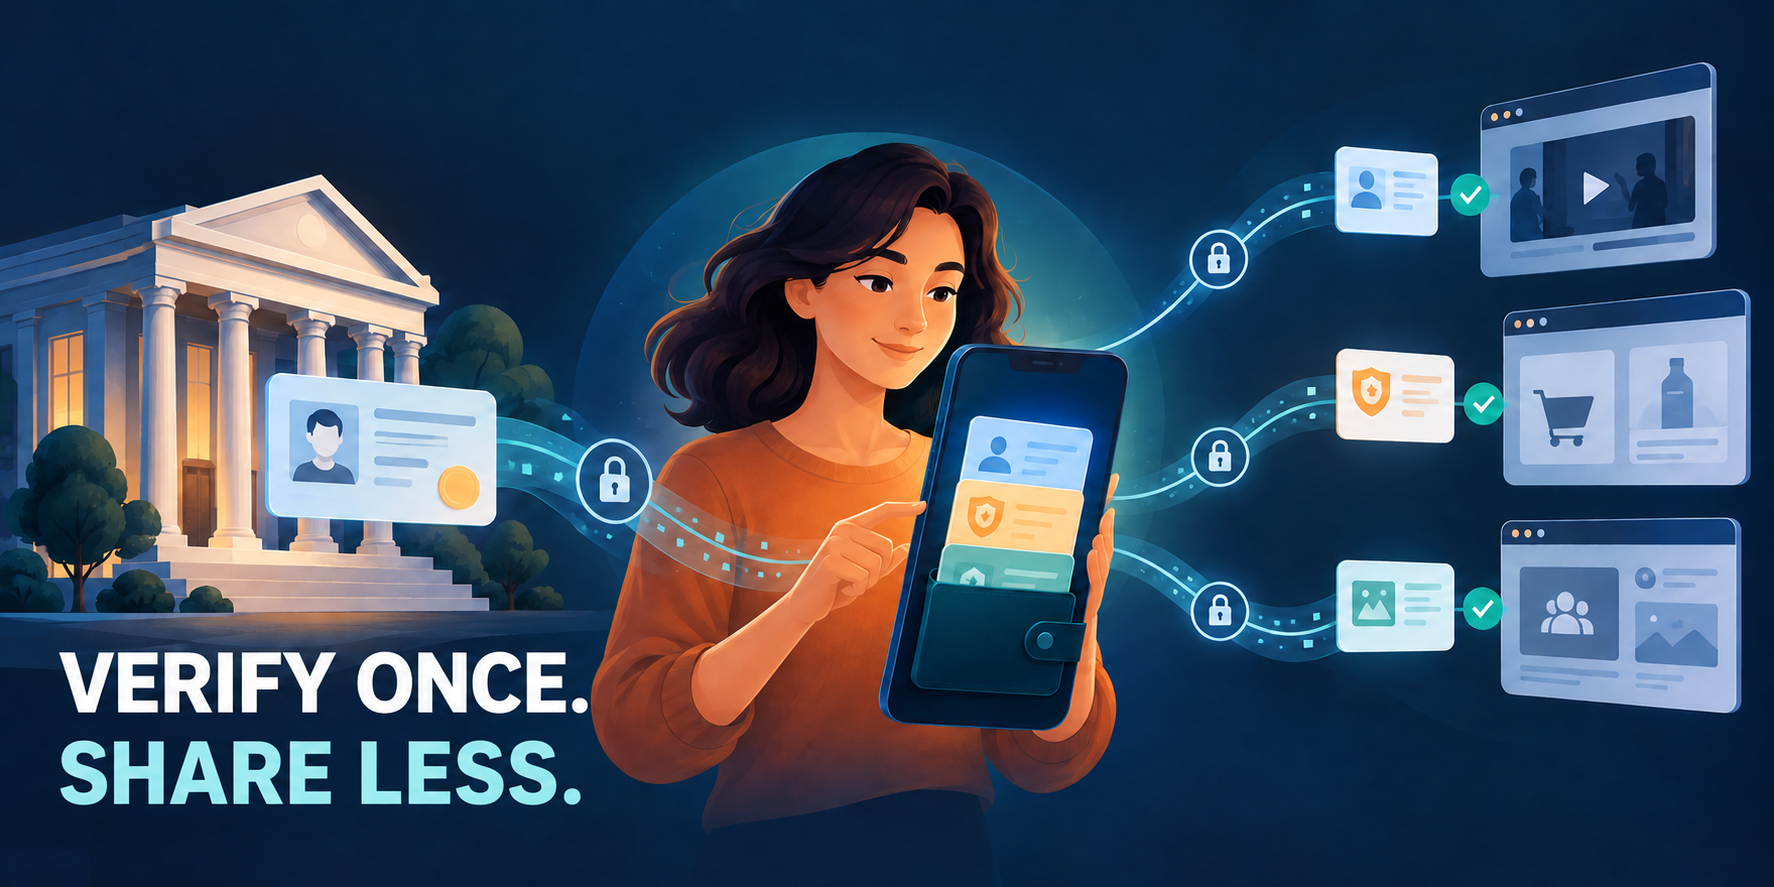
An age-restricted platform has a recurring problem: it needs to know whether a person meets an age threshold, but it should not need a fresh copy of that person’s identity document every time the person visits a new service.
That is the promise behind portable digital identity. A trusted issuer verifies an attribute, the user keeps or controls the resulting credential, and a platform receives a limited proof when it needs to make an access decision. The model can reduce repeated collection, but it does not remove the platform’s responsibility to decide what evidence it accepts.
The useful question is therefore not “Can this credential replace verification?” It is “What exactly does this proof establish, who issued it, and what decision is our service authorised to make from it?”
The W3C Verifiable Credentials Data Model describes a three-party model: an issuer makes a claim, a holder keeps or presents it, and a verifier checks it. A proof of age might communicate that the holder is above a threshold without disclosing a full date of birth or a copy of an identity document.
That distinction matters. A verifier can confirm that a presentation is authentic and current enough for its policy, while still receiving only the attribute needed for the transaction. The credential can be machine-readable and tamper-evident, but “verifiable” does not mean that every verifier must trust every issuer or accept every claim. The receiving platform still evaluates the issuer, the proof, the subject, and its own rules.
Repeated document collection creates friction for users and expands the amount of sensitive information that each platform must handle. A reusable result can support a shorter flow for a person who has already completed a suitable check elsewhere.
For example, imagine a user who has verified that they are over 18 with an approved issuer. When that user opens an adult-content platform, the platform could request a proof of the relevant threshold. The user reviews the request and consents to share it. The platform receives an answer to its access question, rather than automatically receiving the user’s passport number, address, or full birth date.
This is a practical use of digital identity verification: the platform uses a verified result to make a defined decision, while keeping the result narrower than the underlying identity record.
The value is not simply speed. Fewer copies of documents can mean fewer places where a breach, accidental disclosure, or unnecessary internal access could occur. Data minimisation also makes the platform’s explanation to users clearer: it can say what it needs for the decision and why.
Portability does not turn a proof into a universal pass. Before accepting one, a platform should define at least five policies.
Who is allowed to issue the proof, and how does the platform verify that the issuer is genuine? A cryptographic signature helps detect tampering, but it does not answer whether the issuer’s process is appropriate for the platform’s risk and jurisdiction.
Does the proof say “over 18,” provide an age range, or expose a date of birth? The platform should request the smallest attribute that answers its access question. An age result does not automatically establish a person’s legal identity, residency, or eligibility for a financial product.
When was the result issued? Can it be revoked or suspended? Does the platform need a recent result for a high-risk action, or is a longer validity period reasonable for a low-risk content gate?
How does the platform know that the person presenting the proof is the account holder, and that the same presentation has not been copied or replayed? Age assurance and account authentication answer different questions. A platform may need both.
What does the platform record about the decision? A useful audit trail can document the policy version, issuer, time, requested attribute, and result without retaining the underlying identity document. Users should be told what is requested, who receives it, and how long the platform keeps the decision record.
These checks are the difference between a portable proof that supports a clear access policy and a credential that is merely collected because it is available.
Portable identity can support a privacy-first identity verification platform, but the label alone does not guarantee privacy. A platform can still create a detailed profile if it records every request, links presentations across services, or asks for more attributes than it needs.
Good design starts with purpose limitation. A content platform may need only an over-18 result. A marketplace may need a different identity or business attribute. The request should match the decision, and the user should be able to see the requesting party before sharing.
Current European digital-identity work illustrates this direction. The European Commission describes wallets that can hold and present digital documents across public and private services, while age-verification guidance describes a trusted credential being used to generate a proof of a threshold. These initiatives are developing within particular legal and technical frameworks; they do not mean that every service can accept every wallet or that a single result satisfies every rule.
The data-protection question also remains broader than document storage. A platform should consider correlation, retention, access controls, error handling, and what happens when a user declines a request. A smaller data payload is helpful, but it must sit inside a proportionate governance process.
Reusable proofs can reduce repeated uploads and support secure identity verification without data exposure when the platform receives only the result needed for its decision. They do not eliminate the need to understand the original verification method, the issuer’s trustworthiness, or the platform’s own obligations.
They also do not remove the need for recovery and exception paths. A user may lose access to a wallet, use a credential that has expired, or encounter a service that does not yet recognise the issuer. A responsible flow explains the available alternative and avoids turning a technical failure into an unexplained denial.
For ProperUser, the relevant product question is how a platform requests and manages a verified result in a way that leaves the user in control of sharing. ProperUser’s public materials describe requests for verified information such as identity, age, and location. Teams evaluating a deployment should still confirm the exact supported workflow, evidence, retention, and language needed for their own service before making a compliance or security decision.
Before adopting a portable proof of age, ask:
These questions keep portability tied to an actual product and risk decision. They also prevent a familiar mistake: treating a new credential format as a substitute for policy.
Portable digital identity is most useful when it makes a narrow proof reusable under clear conditions. The platform gets an answer it can evaluate, the user shares less than a full identity record, and the issuer remains accountable for the claim it made.
That future will depend on trust lists, interoperable formats, user control, and honest limits. Platforms that define their access question first will be better placed to use reusable proofs responsibly as the ecosystem develops.